Security Catapult is the self-assessment tool our Lead CMMC Assessors built to make CMMC Level 2 preparation clear and manageable. It walks you through each, shows your SPRS score, and tracks the tasks needed to close your gaps.
Built into Catapult is Vanessa, an AI assistant that reviews your documentation and flags inaccuracies and missing items before they affect your score. She’s the same tool our own assessors use.
Vanessa works only with the information you provide. Each assessment is isolated, so your data is never shared with other clients or used to train her.
Upload your System Security Plan (SSP), policies, and artifacts. Vanessa compares your documents, screenshots, and reports against the 320 assessment objectives tied to the Level 2 security requirements in NIST SP 800-171A. She identifies where you meet each objective, when you don’t, and what needs to be deferred for further evaluation.
Her review follows the same methodology Monarch assessors apply on certification engagements. You review and confirm every finding, so a human stays in control of the assessment.
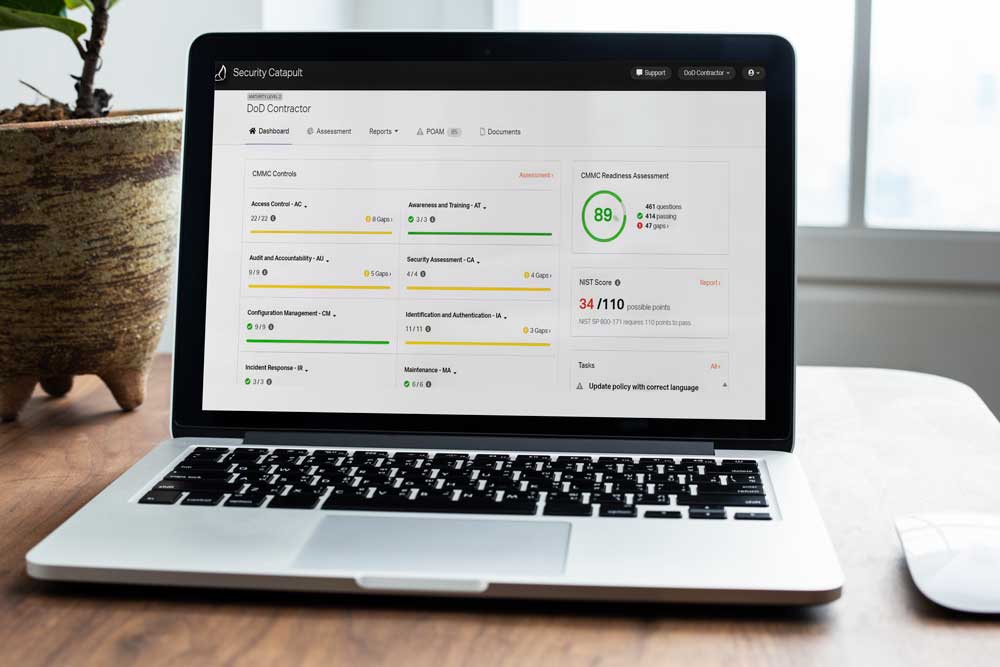
Combining the power of our AI engine, Vanessa, to organize, scan, and identify precise compliance indicators – with the expertise of an assessment tool used by Monarch’s own certified assessment team – Security Catapult provides reliability and accuracy at a level other self-assessment tools cannot. It can:
Upload your evidence into the secure platform and let Vanessa evaluate against the 320 CMMC Level 2 assessment objectives. You review and confirm the findings, then get your SPRS score and POA&M.
Address gaps and work the Plan of Action and Milestones (POA&M). Re-upload evidence as remedies are completed, and let Vanessa reassess your score.
When your self-assessment score meets 110 objectives, and you eligible for Level 2 compliance status, share your record with Monarch. Your certification assessment starts with evidence already mapped.
Security Catapult and Vanessa run in Microsoft Azure Government (GCC High). Your documents are processed inside that boundary, and nothing leaves it. Vanessa does not call ChatGPT, OpenAI, or any service outside that boundary, and she doesn’t learn from or reference other business’s assessments. Every uploaded artifact is hashed on receipt, and you can export the integrity manifest at any time to prove your evidence has not changed since you uploaded it.
When your self-assessment is complete, you are able to share it with our experts. A certified assessor from Monarch ISC can review Vanessa’s findings, your confirmations, and your evidence – and return a signed readiness letter. It is the same review we would do before scheduling a certification assessment. While not required, this helps your organization demonstrate compliance and prepare for certification by a C3PAO.
Vanessa, Security Catapult’s AI engine, produces preliminary findings. Every finding and score remains subject to user review and confirmation, allowing potential errors or misinterpretations to be identified and corrected before the results are finalized. It is also important to understand that our Security Catapult platform does not make you CMMC certified.
While Security Catapult allows you to assess your CMMC Level 2 compliance readiness, it is important to understand that certification is awarded by a C3PAO, or, where your contract allows, from your own affirmed self-assessment in SPRS. Asking Monarch ISC to review the results with our optional assessor review makes your assessment defensible.
Security Catapult is licensed annually and costs are determined by your organization’s size. Every license includes unlimited users, unlimited document uploads, and Vanessa assessment of all 320 objectives. If you choose to include it, our optional assessor review is priced per engagement.
Reach out to the Monarch ISC team to learn more about our Level 2 CMMC Self-Assessment Tool with built-in AI. We can answer any questions, provide a product demo, or offer a quote to license Security Catapult for your organization. Contact us today.
A Note on AI (Artificial Intelligence): Vanessa is an AI-powered assistant designed to help identify potential evidence matching NIST 800-171 Rev 2 objectives. Vanessa can make mistakes, may miss relevant evidence, and may flag content that does not actually satisfy an objective. Her output is intended to support – not replace – the professional judgment of a qualified assessor. All findings, evidence mappings, and assessment determinations should be independently reviewed and validated by a 3rd party assessor before being relied upon. Vanessa does not make certification decisions.
Security Catapult operates in a Microsoft Azure Government environment. Vanessa uses Azure OpenAI Service within the configured environment to process documents submitted for assessment. Your organization’s data should only be uploaded when your use of the platform and your assessment scope meet your organization’s applicable security and contractual requirements. Data never leaves this environment, and Vanessa is configured to never share data with outside sources.
No. Security Catapult is a self-assessment tool and does not issue CMMC certification or CMMC Status. The tool can help your organization evaluate its implementation of the 110 CMMC Level 2 requirements and the associated 320 assessment objectives.
For Level 2, the SPRS score is calculated on a scale of 110 points. A score of 88 or higher may qualify an organization for Conditional CMMC Status when the remaining unmet requirements are eligible for a POA&M and all other applicable requirements for that status are satisfied. A score of 110 represents a final score with all requirements assessed as MET. Whether your organization needs a Level 2 self-assessment or a C3PAO certification assessment depends on the requirements applicable to your contract or solicitation.