Our experienced team brings a passion for cybersecurity excellence and CMMC compliance to help organizations reduce risk and improve results.
At Monarch ISC, our team brings decades of combined experience in cybersecurity, information security, risk management, and regulatory compliance. We help organizations navigate complex security challenges with practical guidance, strategic insights, and solutions aligned with their business goals. From strengthening information security programs to preparing for regulatory assessments – our experts work to make cybersecurity clear, manageable and effective.
For government contractors and organizations across the Defense Industrial Base (DIB), our team provides specialized expertise in Cybersecurity Maturity Model Certification (CMMC) requirements. As a Certified Third-Party Assessment Organization (C3PAO), Monarch ISC understands the challenges defense contractors face when preparing for CMMC certification. Our consultants and assessors help organizations understand requirements, identify gaps, strengthen security practices, and prepare for the assessment process.
We support organizations in the financial, healthcare, defense, and other industries with a range of cybersecurity and information security services, including:
By combining technical knowledge with a collaborative, business-focused approach, we help clients build security programs that address their unique risks, operational needs, and long-term objectives.
Our cybersecurity consultants, assessors, and advisors bring diverse professional backgrounds and specialized knowledge to every engagement. Led by an experienced leadership team with deep industry knowledge, our professionals apply their expertise and knowledge to help clients address complex cybersecurity, risk management, and compliance challenges. Together, we deliver practical guidance and hands-on support tailored to each organization’s needs.
With over 25 years’ experience in IT and information security, Joe Kurlanski has developed sustainable risk management and information security programs for hospitals, banks, credit unions, Department of Defense contractors, and other businesses of all sizes.
Joe founded Monarch Information Security Consulting in 2014 expressly to meet the unique needs of businesses grappling with today’s myriad of laws, regulations and data security challenges. He holds a CISSP® certification from (ISC)² and is a Certified CMMC Assessor (CCA), Provisional Instructor (PI), and Registered Practitioner (RP) with the Cyber AB.
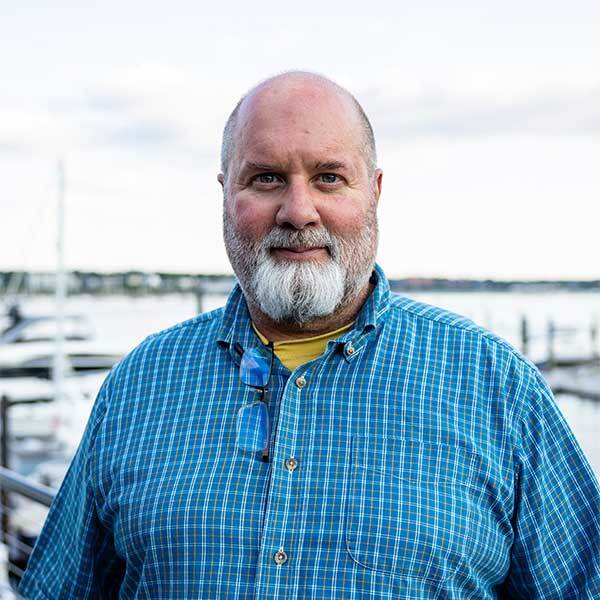
John Rogers, CISSP®, Lead CCA, PI, has 25 years’ experience in cybersecurity, and loves the field. He is also grateful for the relationships sustained with coworkers and clients. John’s focus includes helping clients develop, manage, and assess risk-based security programs that integrate with core business strategies, withstanding regulatory examination, audit, and the test of time. Whether serving as senior advisor, virtual CISO, or member of a board committee, he is trusted to consistently deliver sound advice and excellent work. As a sought-after public speaker, John uses humor and stories from the field to remove fear from this critical subject matter, help his audience relate to it, and feel empowered to contribute as individuals regardless of their role.
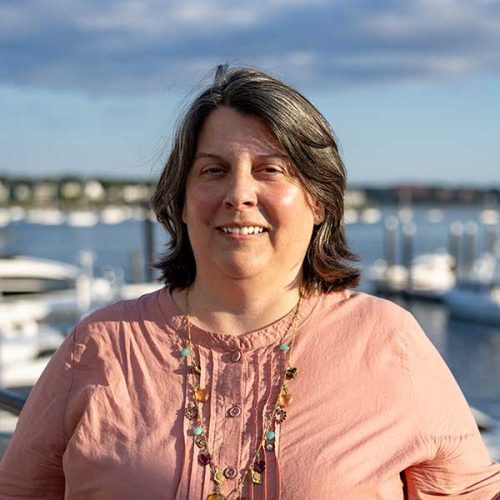
Amy Beth, Lead Certified CMMC Assessor (CCA), CISSP®, CISA®, and ITIL® Foundations certified, brings over 25 years of experience in healthcare compliance, technology, and revenue management. Her expertise spans implementing, managing, and monitoring management systems aligned with widely adopted ISO and NIST frameworks, as well as HIPAA, SOC 2, and PCI DSS requirements. She has led information system assessments, supported enterprise tool selection and implementation, and driven audit readiness across multiple standards.
Amy Beth’s work focuses on aligning business and security goals through clear documentation, effective process design, and cross-functional audit preparation. She has successfully supported large OEM certification programs with vendors such as Cisco, Dell, and AWS, and was part of one of the earliest joint CMMC assessments involving DIBCAC and a C3PAO. Known as a trusted advisor and agent of change, she is valued for her ability to build collaborative momentum and sustain long-term compliance.
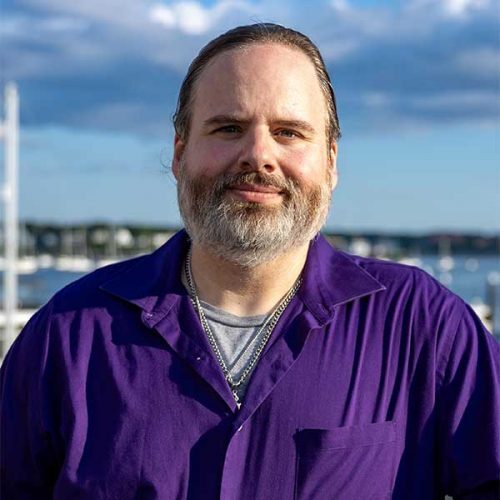
Justin Weeks, CISSP®, CISM®, GXPN®, and Lead Certified CMMC Assessor (CCA), is a seasoned cybersecurity practitioner with more than a decade of experience navigating complex technical, cybersecurity, and compliance landscapes. He has led successful engagements across the Defense Industrial Base (DIB), healthcare, finance, legal, construction, manufacturing, managed services, and professional services sectors. Justin has advised organizations on NIST SP 800-171, NIST SP 800-53, HIPAA, HITRUST, and CMMC—guiding clients toward audit-ready, business-aligned outcomes that strengthen their cybersecurity posture while reducing operational burden and maintaining compliance readiness.
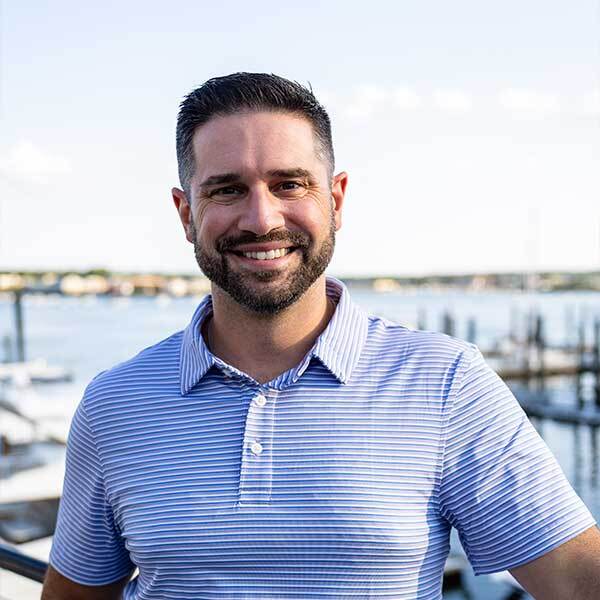
For over a decade, Jim has assisted diverse clients across the private & public sector, including healthcare, finance, and DoD contractor industries. Jim holds a Certified Information Security Management (CISM®) certification from ISACA®. Coming from a long family history of military service, Jim is passionate about helping clients build adaptive cybersecurity programs that practically address compliance challenges and help them further their business goals.
With over 15 years of digital marketing experience, Katie has specialized in developing and executing innovative digital strategies across a variety of industries, including healthcare, non-profits, B2B, and SaaS. Throughout her career, Katie has focused on leading cross-functional teams, optimizing processes, and delivering projects that meet organizational goals. She is skilled in data analysis, process development, and creating workflows that ensure successful and efficient project execution. Known for her collaborative approach, Katie is committed to driving effective outcomes and supporting team success in every project she takes on.
With over 20 years of experience in executive support, Terra brings a strong background in managing executive operations and travel coordination, with a focus on making day-to-day work more efficient. She’s organized, detail-oriented, and brings a clear, structured approach to everything she takes on. Her previous roles as an executive administrator, travel coordinator and HR generalist have given her a solid foundation to support our team’s operations and keep things running smoothly. Terra is passionate about bringing organization into everything she does and continues to build on her knowledge of business operations and executive support.
Choosing a cybersecurity consulting partner means finding a team that understands the technical demands of information security, the nuances of complex compliance requirements, and the realities of running a business. At Monarch ISC, we combine deep expertise with a collaborative approach to help organizations make informed decisions, address risks, and move forward with confidence. Government contractors, DoD suppliers, financial institutions, and healthcare organizations choose Monarch ISC because of our:
Whether you’re a government contractor preparing for CMMC requirements or an organization looking to strengthen its overall cybersecurity program, Monarch ISC can help you determine the right path forward.
Contact our team to discuss your cybersecurity and compliance needs.